Gartner Identifies 12 Audit Hot Spots for 2027

Gartner has identified 12 key risk areas that Chief Audit Executives (CAEs) should consider when developing their 2027 audit plans. The research groups the risks under three broad themes: pressure to realise AI value, strains on IT governance and oversight, Read More …
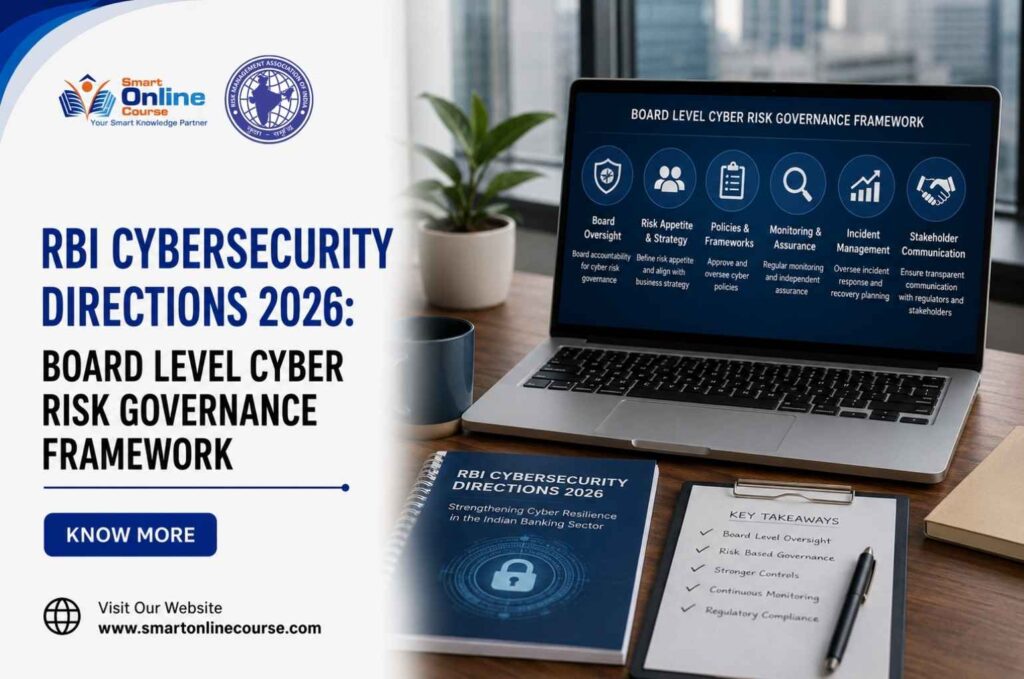
RBI Cybersecurity Directions 2026: Board Level Cyber Risk Governance Framework

RBI Cybersecurity Directions 2026

On 31 July 2026, the Reserve Bank of India issued the Reserve Bank of India (Commercial Banks – Cybersecurity, Technology: Risk, Resilience and Assurance Framework) Directions, 2026, replacing the existing patchwork of cybersecurity instructions with a single framework. This is Read More …

IIM Researchers Develop Framework to Simplify SaaS Adoption in Regulated Sectors

Researchers from IIM Lucknow, Amritsar, and Kashipur have unveiled a groundbreaking risk assessment framework designed to streamline the adoption of Software-as-a-Service (SaaS) technologies in India’s capital markets and banking sectors. Addressing Barriers in SaaS Adoption Globally, SaaS—cloud-based services that deliver Read More …